SOX and File Transfers: Controls for Financial Data
"The auditors would like twenty minutes with whoever administers the interface server." The email from the finance controller arrives on the third day of Acme's quarter-end close. Subsidiaries are uploading trial balance files to the SFTP server. The payroll provider has dropped its usual batch, and the bank files have landed overnight. Nobody at Acme calls it the interface server. It is the transfer server, it is you, and the meeting is about SOX.
SOX is the law that makes executives of publicly traded companies personally attest that their financial reporting is backed by reliable internal controls. It sends external auditors in every year to test whether that attestation holds. Most of the law is about accounting. But financial numbers live in systems, and systems are fed by files. A file feed that could be silently altered, lost, or run by the wrong person makes the numbers downstream untrustworthy. That is the entire logic by which an accounting law reaches your transfer server.
This article translates what SOX-driven audits expect from file transfers. It covers the concept of IT general controls, and the access and change-management disciplines auditors test. It covers the completeness and accuracy checks that make a feed trustworthy, and the evidence you will be asked to produce. It is part of our Compliance Frameworks series — education for the admin's side of the table, while your finance team and auditors own the official interpretations.
Why an Accounting Law Reaches Your Transfer Server
The chain of reasoning explains every question an auditor will ever ask you, so it is worth spelling out. Public companies publish financial statements. Investors rely on those statements, so the law requires internal control over financial reporting — usually shortened to ICFR. These are the processes that give reasonable assurance the numbers are right. The statements are assembled from applications: the general ledger, the ERP, consolidation and reporting tools. Those applications trust their inputs — and their inputs, in most companies, arrive substantially as transferred files.
Auditors therefore care about two layers. Application controls live inside the financial systems: validations, reconciliations, approval workflows. IT general controls — ITGC — are the layer underneath: the controls over the computing environment itself that make it reasonable to trust anything the applications do. If anyone could log into the transfer server and quietly edit the payroll file before the ledger ingests it, no application control downstream can fully repair the damage. ITGC is where the transfer admin lives, and it is tested every audit cycle. Nobody applies to live there; the address comes with the server.
One boundary to respect from the start: you do not decide which feeds matter. Whether a flow is in scope for SOX depends on whether it feeds material financial reporting — a judgment made by finance and the auditors, not by IT. Your contribution is an honest inventory of the feeds that exist (the transfer inventory is the working format) and disciplined controls over the ones designated in scope. If you run transfers at a private company, the law itself may not apply to you. But lenders, acquirers, and auditors of other stripes ask for the same disciplines, so nothing in this article is wasted.
The Close, Seen as File Flows
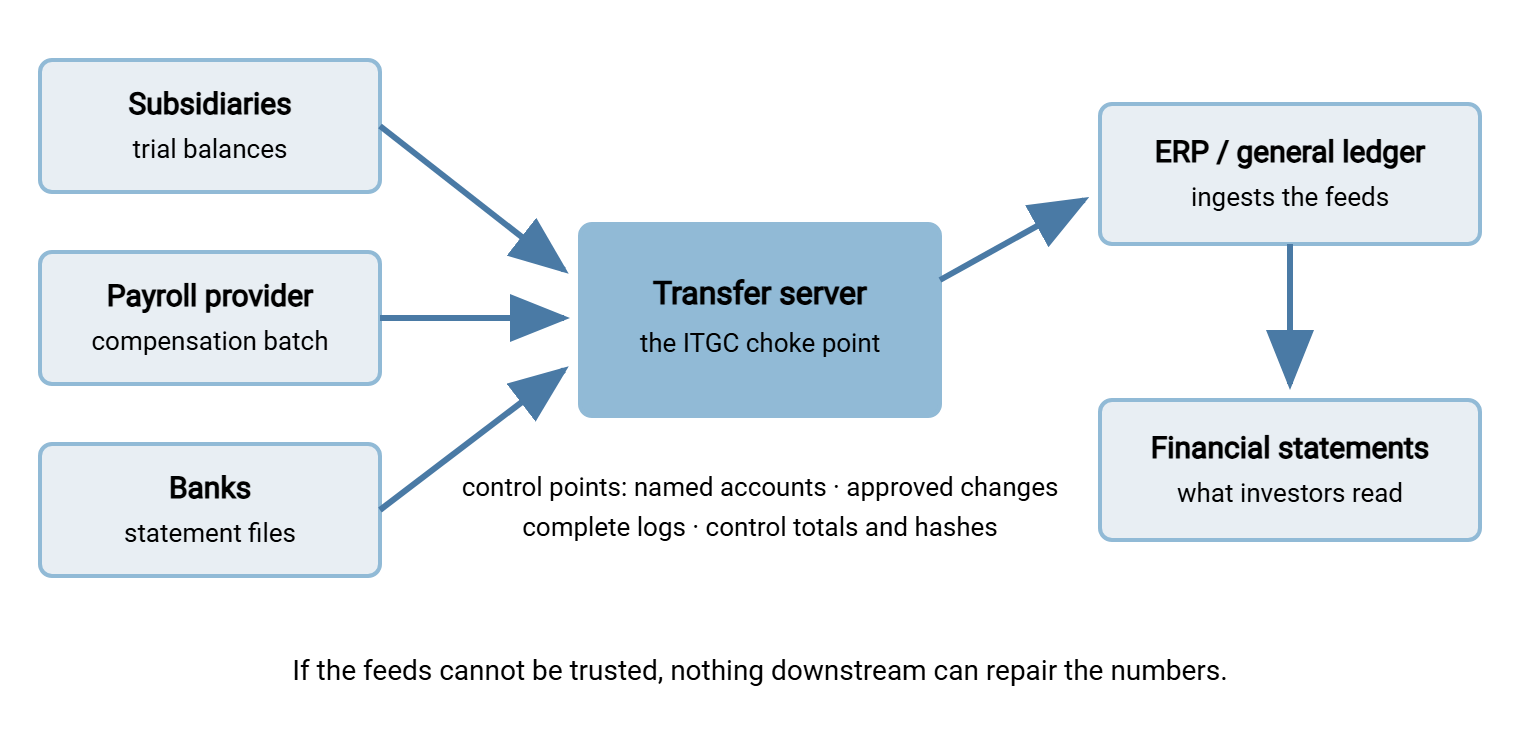
Look at the close the way an auditor does, and it resolves into a set of file transfers, each one a place where the numbers could go wrong:
- Subsidiary trial balances uploaded to the SFTP server on a deadline, then ingested by the consolidation system. Risk: a missing or truncated file understates a whole entity; an altered one misstates it.
- The payroll provider's batch — an outside party writing numbers into your compensation expense. Risk: wrong file, stale file, or a file modified after delivery.
- Bank statement files pulled or received daily, driving cash reconciliation. Risk: incompleteness that hides transactions.
- Journal entry uploads prepared by accountants and loaded into the ledger. Risk: edits between preparation and load, or uploads by people who should not be able to make them.
The diagram below shows this shape: several sources converging on the transfer server, which feeds the financial applications that produce the statements. Every arrow is a control point, and the middle box is where most of them are implemented.
The ITGC Buckets, Translated to Transfer Work
Auditors organize ITGC testing into a few standard buckets. The table below translates each into transfer-server terms, along with the evidence that typically satisfies the question. Keep it: it is a preview of your audit agenda.
| ITGC bucket | The auditor's question | Transfer translation | Typical evidence |
|---|---|---|---|
| Access to programs and data | Who can read or change the feed, and should they? | Named accounts, least-privilege folders, prompt deprovisioning, periodic access review | Account list with owners; review sign-offs; termination tickets matched to disabled accounts |
| Change management | How do job definitions change, and who approved it? | Ticketed, approved, tested changes to schedules, mappings, endpoints; no casual production edits | Change tickets sampled against actual configuration history |
| Operations | Do the jobs run, and does anyone notice failures? | Scheduled jobs with alerting, retry handling, documented reruns, completeness checks | Job logs, failure alerts and their resolutions, reconciliation records |
| Program development | Were new feeds built and approved properly? | New flows designed, tested, and signed off before carrying production numbers | Project approvals; test results; go-live sign-off |
Access: Who Can Touch the Feed
Access is the bucket where transfer servers most often fail, because financial feeds tend to accumulate informal access over the years. There is the analyst who once fixed a file and kept the password. There is the consultant's account nobody disabled, and the "temporary" shared login from a migration. Auditors approach this with a simple model — access should be individual, justified, and current — and they test all three. Informal access never expires; it just stops being mentioned.
Individual means named accounts only. A shared "finance" login makes it impossible to say who replaced the payroll file, which is precisely the question an investigation would need answered. Service accounts for the automated jobs are fine, but each one belongs to a single feed, with an owner and a documented purpose. That discipline is laid out in service account hygiene. Justified means least privilege. Subsidiary accounts can write only to their own upload folder, and ledger ingest can read only the staging area. Nobody has blanket access because it was convenient. The folder-design patterns in least privilege in practice apply directly. Current means departures and role changes propagate to the transfer server quickly. The checklist in offboarding that closes the account is the one to steal. A periodic access review re-certifies the whole list.
A related expectation is segregation of duties. The person who prepares financial data should not also control the pipeline that delivers it. The administrator who can change job definitions should not be the one who approves those changes. In small teams perfect separation is impossible, and auditors know it. The accepted compensation is monitoring: someone independent reviews the logs and changes that the powerful account produced. Tying transfer-server accounts to your directory helps the "current" test enormously. Sysax Multi Server can authenticate against Windows or Active Directory accounts. So disabling a departing employee in the directory closes their transfer access in the same motion. IP allow lists keep partner accounts usable only from partner networks.
Change Control: The Job Definition Is Regulated Territory
SOX asks one mental shift of an admin: the definition of the payroll feed — its schedule, source, destination, file mapping, and post-processing — is not just configuration anymore. It is part of a financial control, and changing it casually is like editing the ledger casually. Auditors will sample changes and ask for the ticket, the approval, the testing, and who moved it to production. Have the ticket. Not the memory of the ticket.
The workable pattern is boring and effective. Every change to an in-scope flow gets a ticket, an approver who is not the implementer, a test against sample files, and a record of when it went live. Emergency fixes are allowed — files fail at quarter-end, reality intervenes — but they get documented after the fact and reviewed, not forgotten. Keep the job definitions themselves somewhere inspectable: scripted, exported, or version-controlled, so "what changed and when" has an authoritative answer. Automation helps here precisely because it turns tribal knowledge into artifacts. A scheduled task in Sysax FTP Automation is a defined, reviewable object — schedule, endpoints, pre- and post-processing steps — rather than a command someone runs from memory. That makes it something a change process can actually govern.
Remember: to an auditor, an undocumented change to a financial feed is indistinguishable from tampering. The control is not "we are careful" — it is a visible trail: request, approval, test, deploy. Build the trail into the routine and quarter-end emergencies stop being audit findings.
Operations: Completeness, Accuracy, Timeliness
The operations bucket asks whether the feeds actually work, reliably, with failures noticed and handled. Three properties matter, and each has a transfer-level control:
- Completeness — everything that should have arrived did. Control totals and record counts travel with the file (the source says "this batch has this many rows summing to this amount"), and the ingest verifies them. File hashes catch truncation and corruption; the pattern of building verification into unattended jobs is covered in integrity in automation.
- Accuracy — what arrived is what was sent. Checksums or hashes computed at the source and verified at the destination, documented in manifests where multiple files travel together, as described in checksum files and manifests. Finance closes the loop with reconciliations, but the reconciliations assume the file layer did its job.
- Timeliness — the file came when the close needed it. Scheduled jobs with retry logic, alerts on failure and on absence (the file that never arrived is the sneakier problem), and documented reruns when something breaks. An email notification that a subsidiary's upload failed at two in the morning is a control; the admin who notices at nine is a delay in the close.
Auditors test operating effectiveness by sampling: pick several close cycles and show that the jobs ran, that the one failure alerted, and that the rerun was recorded. That is only answerable if the routine produces records as it goes — which is the real meaning of "operations as a control."
Acme's version of that trail: on the second night of one close, the subsidiary upload job failed because the partner's server rejected the connection. The failure alert emailed the on-call admin at two in the morning and opened a ticket automatically. She retried at six, and the file landed. The ingest verified the record count against the control total. The ticket recorded all of it: failure, cause, rerun, verification. Months later an auditor sampling that date found the failure in the logs, asked what happened, and received the ticket, which took four minutes. That was a passed test. The identical technical event with no alert, no ticket, and a shrugged "we probably just reran it" is a finding — same night, same fix, different discipline.
Evidence: What the Auditors Ask For
SOX audits distinguish design — is the control sensible on paper? — from operating effectiveness — did it actually run all year? The first is a conversation and a walkthrough; the second is samples and records. Expect requests like the transfer server's account list with access levels, and the access review sign-offs. Other examples are five specific change tickets matched against configuration history, and the transfer logs for a handful of named dates. Another is the alert and resolution for a failed feed the auditors found in those logs.
Two properties make evidence credible. It should be system-generated — exported from the server, with timestamps, rather than typed into a spreadsheet by hand. It should be complete over the period, which makes log retention a first-class setting. Keep transfer logs across at least the full fiscal year plus the audit season, and protect them from casual editing. That protection is the subject of log tamper resistance. A server that logs to both file and database, as Sysax Multi Server does with rollover, gives you a queryable store for producing date-ranged extracts on request. That is the difference between answering an auditor in an hour and in a week. The craft of packaging all this is covered in audit-ready reporting from transfer logs. The custody thinking behind "who touched this file between A and B" has its own series in chain of custody.
When controls slip: the finding ladder
Know what happens when a control misses, because SOX findings come in escalating grades and the vocabulary will be used in front of your management. A control deficiency is the base case: a control did not operate as designed — an access review skipped one quarter, a change that went in without its approval. A significant deficiency is a deficiency, or a pile of them, serious enough to report to the company's audit committee. A material weakness is the grave one: a gap that creates a reasonable possibility a material misstatement would not be caught. It gets disclosed publicly, which is why executives react to the phrase the way admins react to "the backups have never worked."
Where any particular miss lands on that ladder is the auditors' judgment, not yours, and single small items usually stay at the bottom. The pattern to avoid is accumulation. The same transfer-control miss repeating across quarters reads as a control that exists on paper only. Examples are reviews that quietly stopped, or alerts nobody rewired after a mail server change. Paper controls climb the ladder. I have watched an access review that "quietly stopped" cost more hours in the following audit than three years of doing it would have. The practical defense is the one this whole article describes: routines that generate their own records, checked occasionally by someone who is not the person running them. When a finding does land, negotiate remediation you can actually deliver by the agreed date; a missed remediation commitment is remembered far longer than the original finding.
A SOX Transfer Control Checklist
The condensed version for the feeds your finance team designates in scope. It doubles as a self-assessment before the auditors arrive.
SOX TRANSFER FEED CHECKLIST (per in-scope flow)
[ ] Flow documented: source, destination, schedule, owner,
    financial purpose
[ ] Named accounts only; service account per feed with owner
[ ] Least-privilege folders (writers write, readers read)
[ ] Departures propagate promptly; periodic access review
    with recorded sign-off
[ ] Segregation: implementer != approver; powerful accounts
    monitored by someone independent
[ ] Every change ticketed, approved, tested, and traceable to
    the configuration history
[ ] Jobs scheduled with retries; alerts on failure AND on
    missing files; reruns documented
[ ] Completeness and accuracy checks: record counts, control
    totals, hashes verified at ingest
[ ] Transfer logs complete for the fiscal year, protected from
    modification, exportable by date range
[ ] Evidence folder maintained as-you-go: reviews, tickets,
    alerts, reconciliation confirmations
The Short Version, and Where Next
SOX reaches your transfer server because financial statements inherit the trustworthiness of the file feeds beneath them. Auditors test that inheritance through IT general controls. They look for access that is individual, justified, and current, and changes that leave a trail. They look for operations that prove completeness, accuracy, and timeliness, and evidence generated by the routine itself. None of it is exotic — it is the same discipline every framework wants, aimed at the ledger. Twenty minutes with the auditors is plenty when the routine has been keeping the records for you.
For the shared logic across regimes, start at why compliance frameworks care about file transfers. If card data also moves through your estate, PCI DSS and file transfers is the neighboring deep dive. When you are ready to serve several frameworks with one control set, the method is in building a transfer control matrix. The audit meeting itself is the subject of our audit-ready reporting series.
Frequently Asked Questions
We are not a public company. Can we ignore SOX?
What does ITGC stand for, and why does it include my server?
Do auditors really look at file transfer jobs?
Which of our feeds are "in scope" for SOX?
What evidence should I keep during the year?
From the Sysax team: we build secure file transfer software for Windows. Sysax Multi Server is an FTP, FTPS, SFTP, and HTTPS server. Sysax FTP Automation handles scheduled, scripted transfers. Free trials are on the download page.